
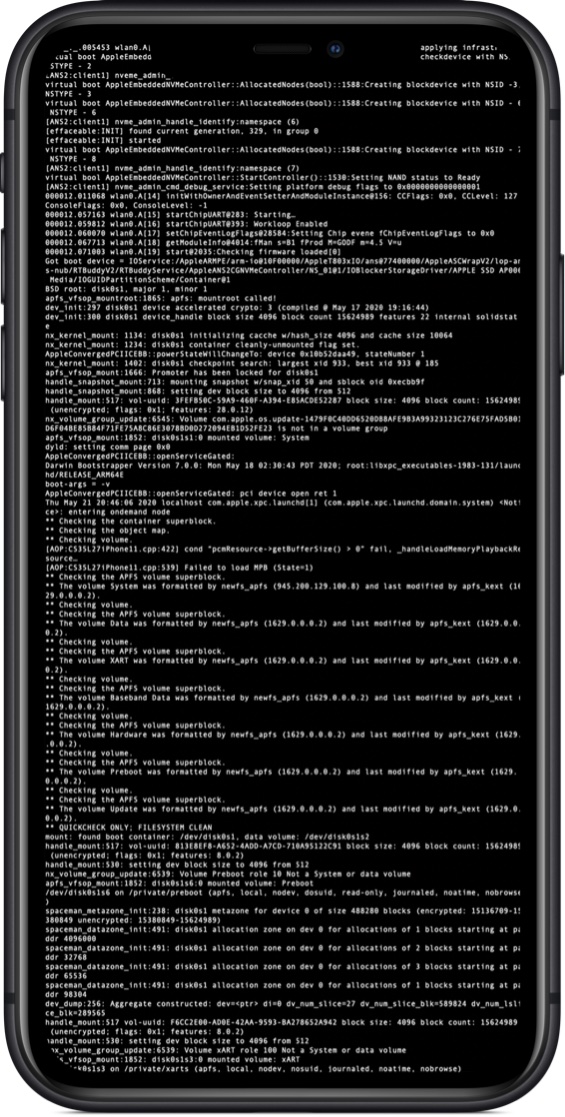
Apple is today launching a new Apple Security Research Device Program that's designed to provide security researchers with special iPhones that are dedicated to security research with unique code execution and containment policies.


Every government in the world just joined the Apple Developer Program.
Requirements include being in the Apple Developer Program, and having a track record finding security issues on Apple platforms.

There's a huge difference. Right now there's no way to inspect the file system to see if there was a successful breach, and crash logs only contain a stack trace and memory snapshot of application. With this kit you have full access to the device that normally would be protected. This lets you probe more sensitive areas such as Secure Enclave.How is this different than the crash logs we already have in iOS?
Security researchers are sometimes government funded though. They can’t survive just on bug bounties.This is great news!
I think we will be ok.


It's their product, and it's their hardware, why wouldn't you give all the control and timeline to Apple?The big issue is, that Apple controls everything in this programme. Apple could decide not to fix an issue and nobody would know because only Apple decides when to release the information. That is btw the reason why Google's Project Zero won't join this programme, it is against their 90 days publication policy.
It's their product, and it's their hardware, why wouldn't you give all the control and timeline to Apple?


